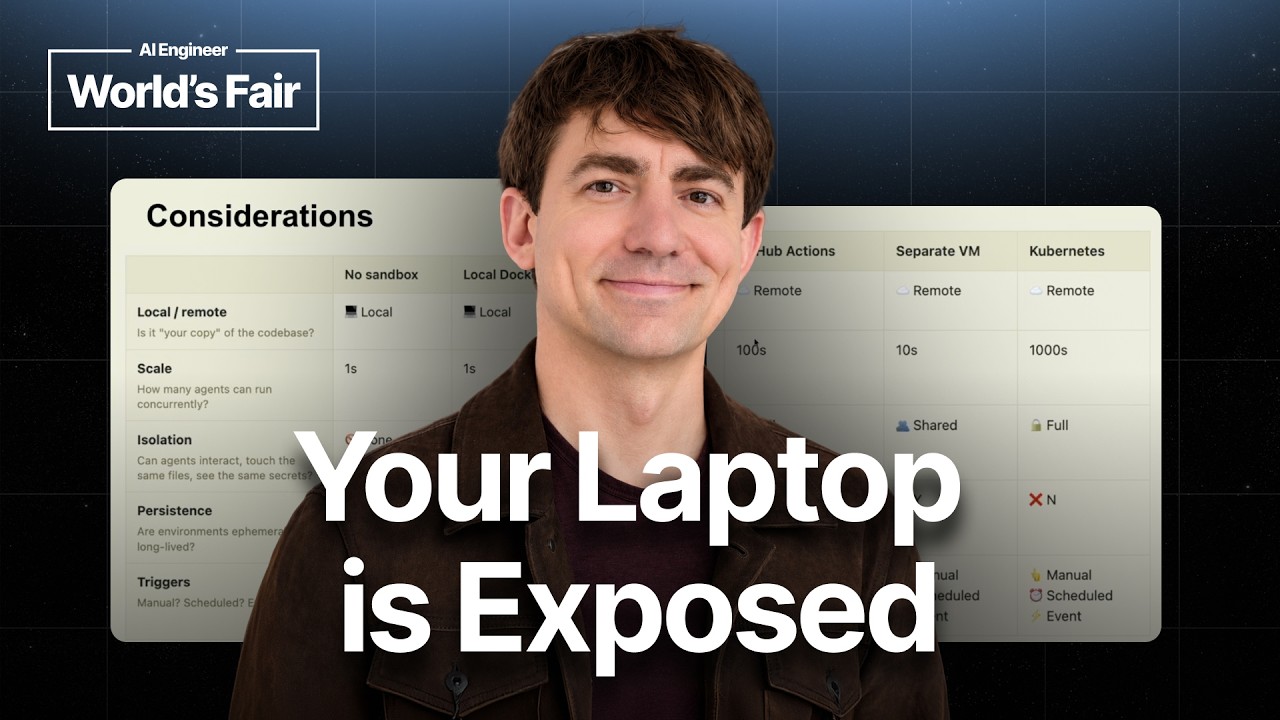
Robert Brennan, CEO of OpenHands, discusses the critical importance of sandboxing coding agents as AI-driven development evolves. He traces the progression from simple code snippet generation by chatbots to sophisticated AI agents capable of writing, running, and debugging code autonomously. Brennan highlights the shift from developers running agents locally on their machines to organizations deploying these agents in the cloud, which necessitates robust sandboxing to control agent access and ensure security.
Running coding agents locally presents significant security challenges. Developers often face a trade-off between manually supervising agents with restricted permissions or enabling broad access through risky “dangerously skip permissions” modes. In the latter case, agents can access the entire local file system, environment secrets, and even production databases, posing substantial risks. Brennan emphasizes the principle of least privilege, advocating that agents should only have access to the minimal resources necessary to perform their tasks to limit potential damage from errors or malicious behavior.
Brennan outlines four main strategies for sandboxing coding agents. The first involves running agents inside Docker containers on local machines, providing ephemeral, isolated environments that can be easily reset if compromised. The second strategy uses cloud-based GitHub Actions, which offer scalable, ephemeral environments with built-in secrets management but are limited to GitHub event triggers and proprietary infrastructure. The third approach involves dedicating a virtual machine or physical device to run agents, allowing persistence and broader event handling but risking co-location issues where multiple agents share access and can interfere with each other.
The fourth and most robust strategy Brennan presents is leveraging Kubernetes or similar cloud-native orchestration platforms. This approach provides highly scalable, ephemeral pods for each agent session, ensuring strong isolation, easy cleanup, and the ability to respond to diverse event triggers from multiple systems like Slack, GitHub, and DataDog. Kubernetes enables running thousands of agents concurrently with fine-grained access control, making it ideal for fully automated, cloud-based AI development workflows.
Finally, Brennan cautions that sandboxing is not foolproof, citing instances where agents have escaped their sandboxes due to container vulnerabilities or outdated software. Despite these risks, sandboxing remains a vital first line of defense. He also promotes OpenHands Agent Canvas, a flexible platform that supports running agents across various sandbox environments—from local Docker containers to remote VMs and Kubernetes clusters—allowing developers to choose the best setup for their needs and gradually transition from local to cloud-based agent workflows.
Useful Links